

Bloom Trading customers suffered practically $1 million in reported cryptocurrency losses after a suspected safety breach drained dozens of Solana wallets on the twenty sixth of October.
The incident affected 49 wallets, elevating issues concerning the safety of Telegram-based cryptocurrency buying and selling platforms.
Bloom Trading confirms third-party vulnerability behind $947K theft
Reportedly, an attacker drained 9,408 SOL, valued at roughly $954,000.
The incident concerned the biggest particular person pockets lack of 1,636 SOL (about $166,000), underscoring the gravity of the scenario.
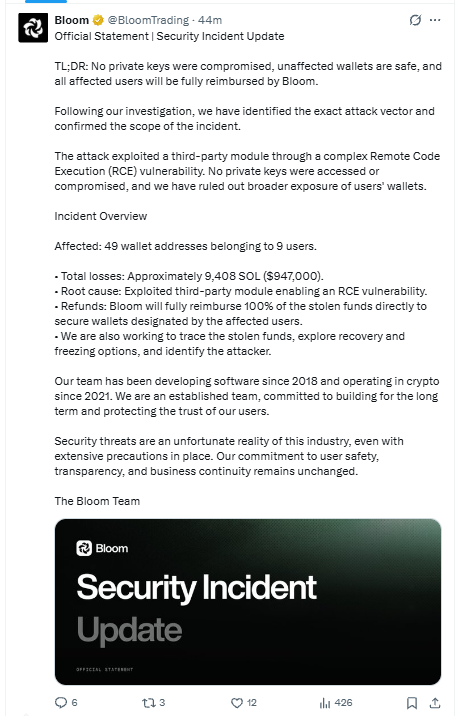
Bloom Trading later clarified that 49 addresses had been affected, belonging to 9 customers.
After investigation, Bloom Trading discovered that the assault got here from an exploited third-party module.
The vulnerability reportedly enabled distant code execution, which might permit for operating instructions within the software program surroundings with out authorization.
The firm assured that wallets not affected had been nonetheless protected, suggesting the breach was restricted to the recognized addresses.
Bloom Trading promises 100% reimbursement
After confirming the reason for the assault, Bloom Trading reiterated its dedication to the compensation of all 9 affected customers.
The platform additionally said that it could ship the stolen cash straight to newly created protected wallets, saying,
Bloom will absolutely reimburse 100% of the stolen funds immediately to safe wallets designated by the affected customers.
Beyond the reimbursement, the crew had begun the method of tracing the stolen property and contemplating restoration, which can contain fund freezes.
The firm, nevertheless, was but to specify when reimbursements could be accomplished.
Bloom guidelines out private-key publicity following investigation
The latest updates additionally answered questions concerning the pockets safety practices of Bloom Trading.
Bloom is a buying and selling automation service on the Telegram platform, which works with the Solana [SOL] and Ethereum [ETH] Virtual Machine networks.
These forms of platforms is likely to be susceptible to safety threats due to software program integrations, particularly if third-party parts have vulnerabilities that may be exploited.
Bloom’s investigation, nevertheless, attributed the incident to an RCE vulnerability, not to compromised personal keys. .
The firm said,
No personal keys had been compromised, unaffected wallets are protected, and all affected customers shall be absolutely reimbursed by Bloom.
Bloom additionally emphasised its longstanding software program growth expertise and dedication to sustaining enterprise operations.
Recent crypto safety incidents spotlight wider vulnerabilities
The incident got here after a number of cryptocurrency safety warnings had been reported throughout October.
Earlier, AMBCrypto reported a important XRP vulnerability that Ripple patched earlier than attackers might exploit it.
The vulnerability may need allowed the theft of trillions of XRP from only one transaction.
Separately, a suspected NBA Instagram compromise raised issues after the account promoted a Solana-based memecoin.
While these incidents concerned totally different safety threats, they highlighted vulnerabilities throughout cryptocurrency infrastructure and digital platforms.
Final Summary
- Bloom Trading traced the $947K theft to a third-party software program vulnerability affecting 9 customers.
- Full reimbursement is promised, however stolen fund restoration and compensation stay pending.


