
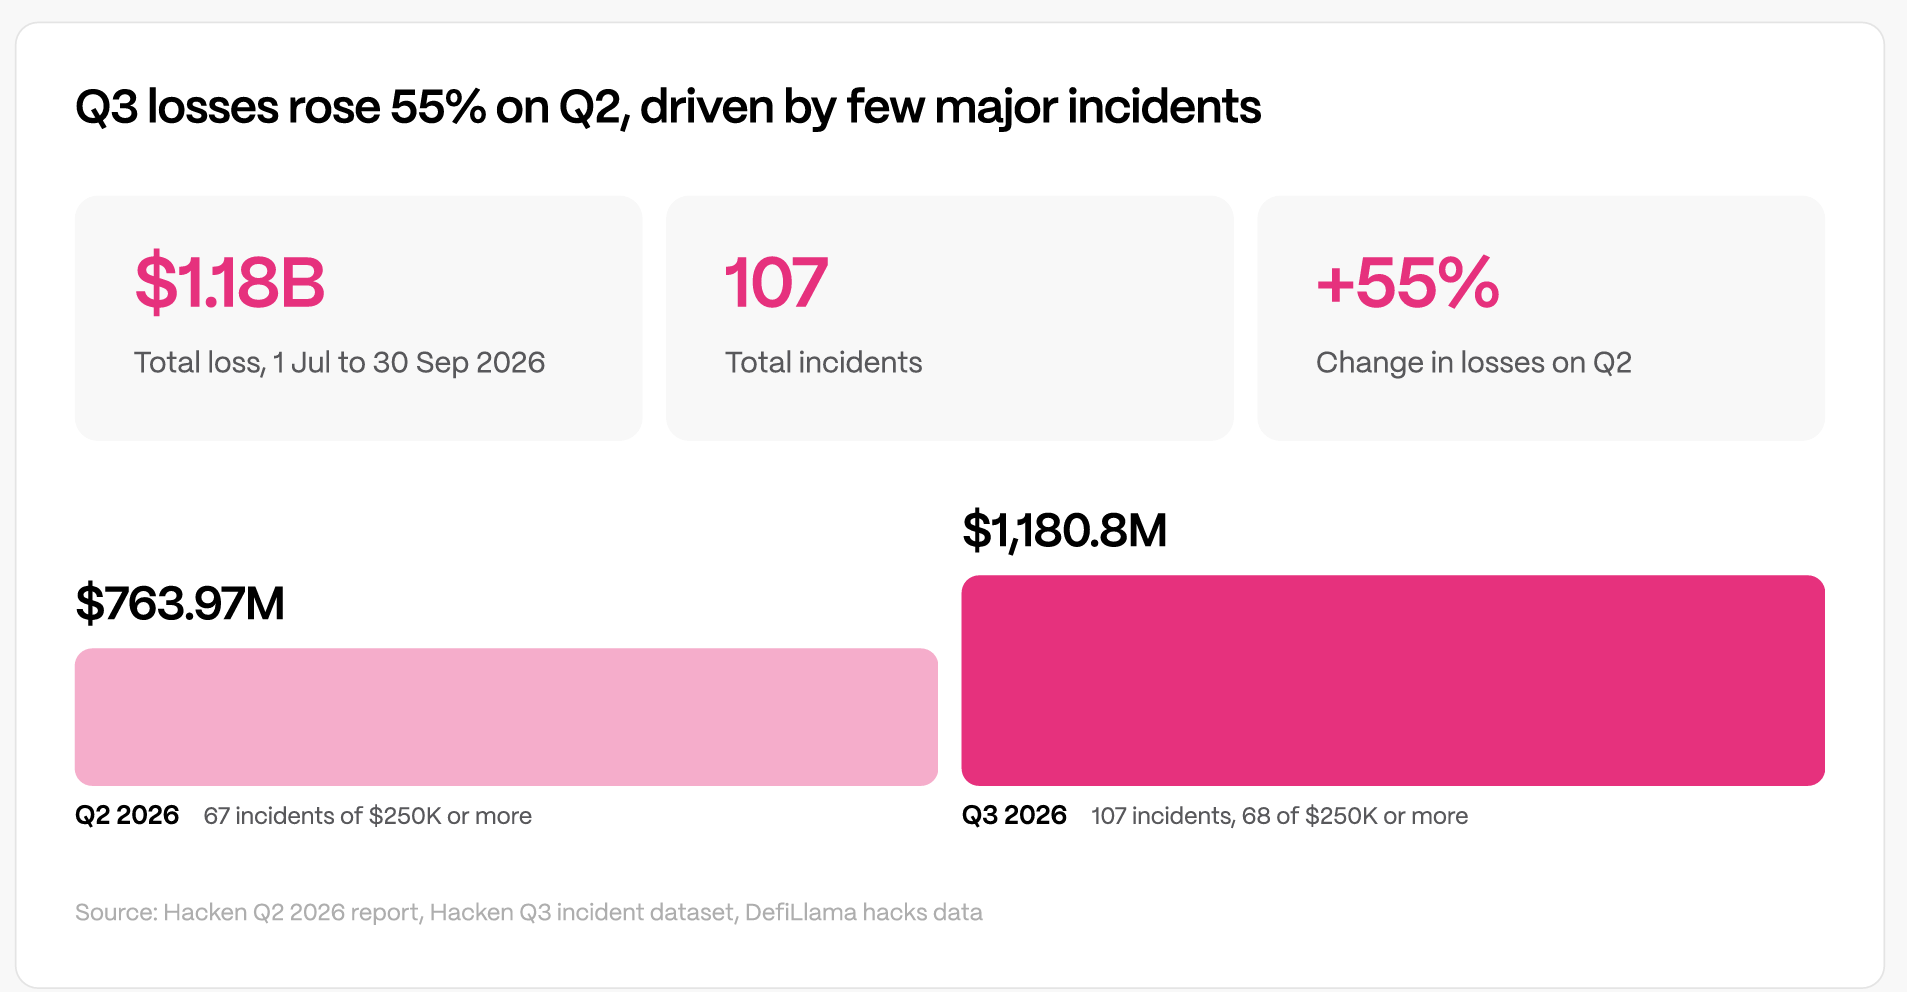
Crypto safety dangers intensified in Q3 2026, as each the quantity of incidents and the monetary harm elevated. Losses grew by an astonishing 55% to $1.18 billion from $ 763.97 million. This was a staggering 40% progress charge that occurred throughout one quarter.
Moreover, the quantity of reported breaches grew from 67 in Q2 to 107 in Q3. Of these 107 breaches, 63 had been related to losses exceeding $250,000.
Therefore, it seems that this represents a rise in potential vulnerability in addition to rising monetary danger. However, there’s proof that the majority of the harm has been restricted to fewer large-scale incidents.
Additionally, compromised suppliers, delayed patches, and un-audited elements had been chargeable for 77% of losses, price $906.8 million.
Therefore, it’s evident that hackers are exploiting vulnerabilities past the easy exploitation of sensible contract code. They are exploiting vulnerabilities inside third-party programs and operational processes.
Stronger audits should subsequently embody suppliers, well timed patching, and steady monitoring throughout linked infrastructure.
The flaws behind Q3’s crypto losses
These broader safety gaps change into clearer when analyzing how attackers exploited particular weaknesses and the way a lot every failure price. Smart contract defects led to 79 reported breaches, which resulted in roughly $569.5 million in losses.
On the different hand, entry management and operational failures resulted in a mere 22 breaches totaling $477.6 million. Therefore, they produced extra monetary affect per breach.
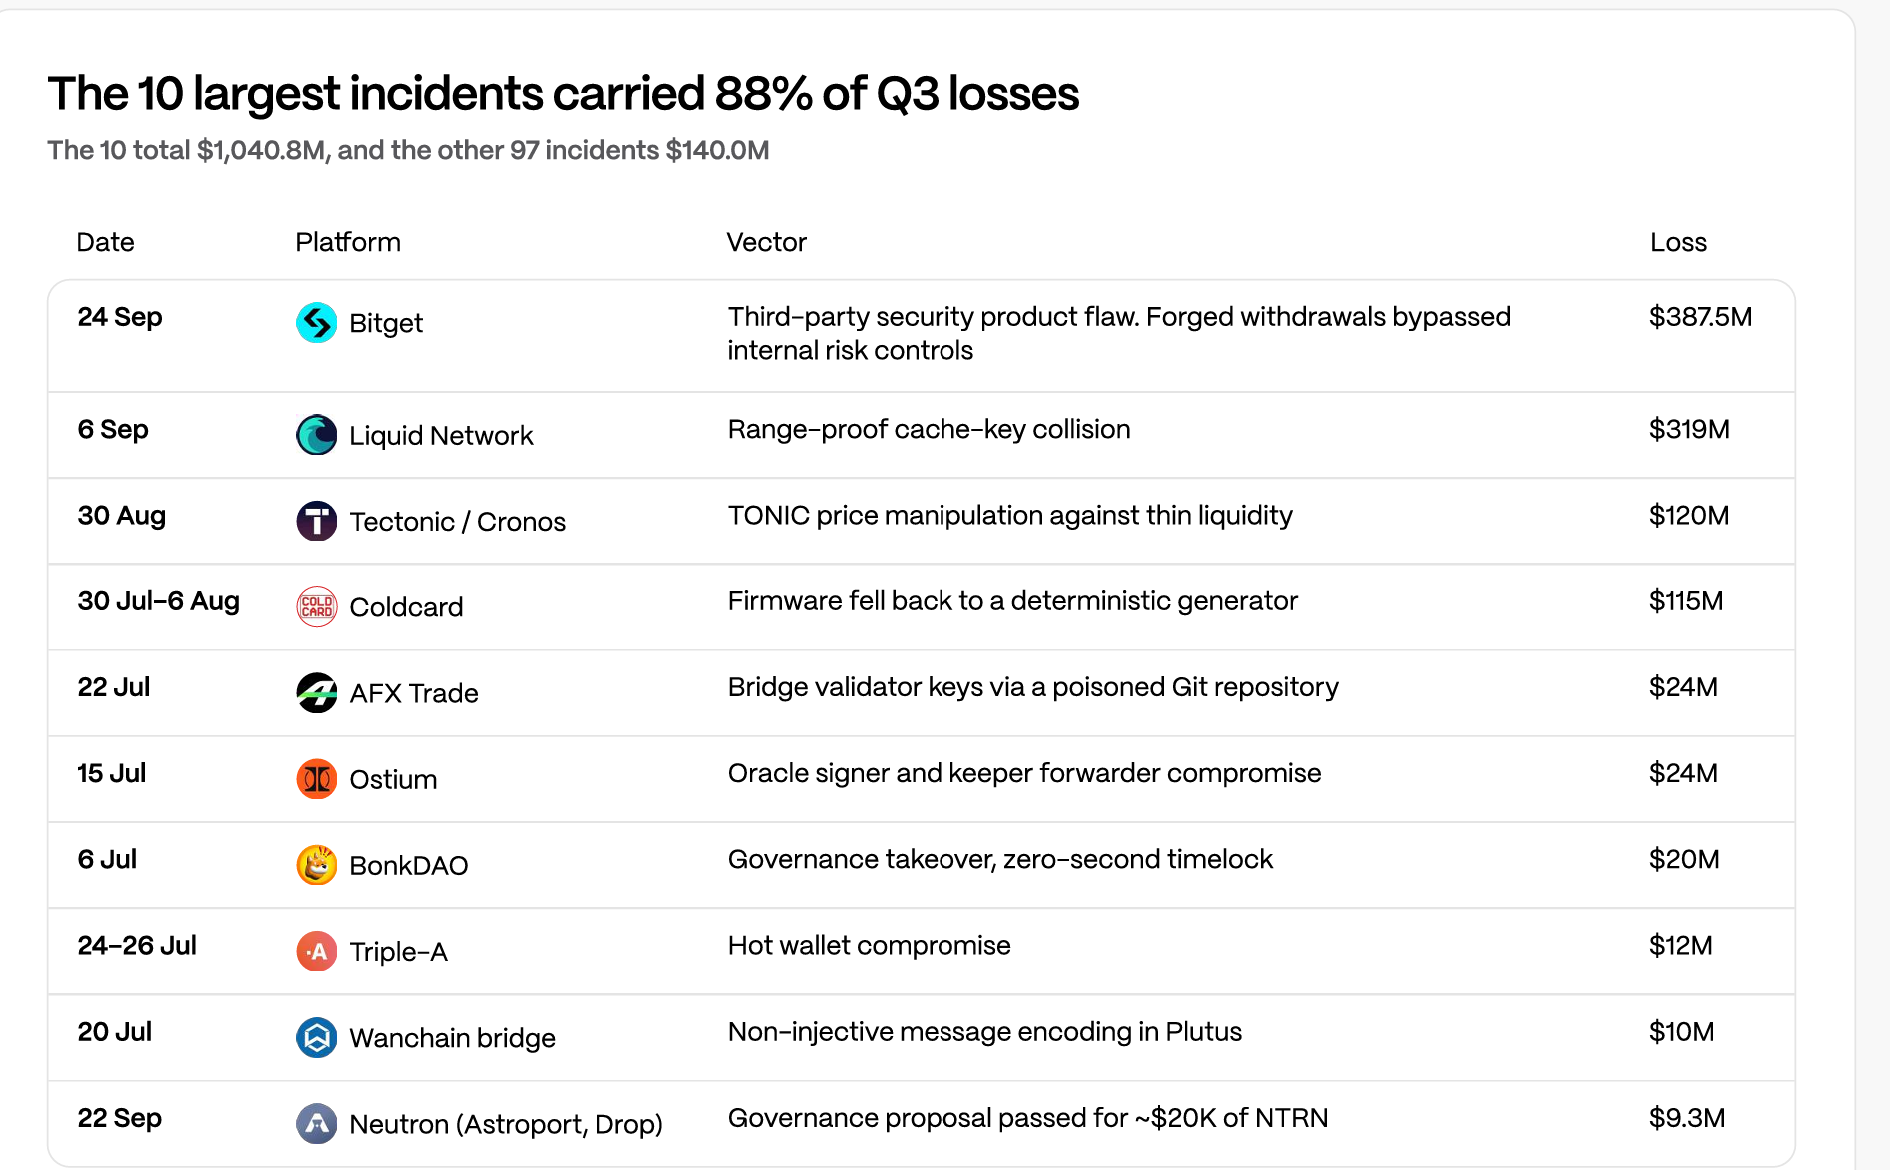
Bitget accounted for the greatest loss, dropping roughly $387.5 million. This was after hackers exploited a zero-day flaw in a third-party safety software program bundle to generate fraudulent withdrawal requests.
Additionally, the Cosmos EVM chain misplaced roughly $5.7 million because of its failure to implement a safety replace inside 96 days of its launch. This created a window of alternative for underflow exploits towards chains that had not but carried out the safety replace.
Similarly, Coldcard suffered $111 million in losses after a construct test flaw launched a weak point into {hardware} pockets seed technology. However, this sort of error ought to have been recognized and addressed by means of correct software program configuration procedures earlier than use.
Can monitoring cease crypto hacks?
With the causes of these assaults clear, wanting ahead, the subsequent query is whether or not steady monitoring can cease related losses. According to Hacken analysis, attackers exploited weaknesses even after safety fixes turned public.
This means that corporations usually didn’t act shortly sufficient, moderately than failing to establish the dangers. Continuous monitoring may assist groups observe new threats, repair pressing weaknesses, and ensure that updates attain all affected programs.
For crypto companies, these adjustments may cut back theft, restoration prices, and repair disruptions. Ultimately, fixed monitoring must consequence in a faster response time for addressing potential points earlier than they change into precise issues.
Final Summary
-
Crypto safety losses rose 55% to $1.18B in Q3 2026, with infrastructure and patching gaps driving 77% of losses.
-
Crypto companies want steady monitoring and quicker patching to forestall repeat assaults and cut back monetary harm.